Why Alethor encrypts the document instead of just deleting it, and what this protects for BPOs
An incorrect value entered your system. Was the document wrong, or did the reading fail?
If the original and the extracted data have already been deleted, no one can answer. Neither you, nor us.
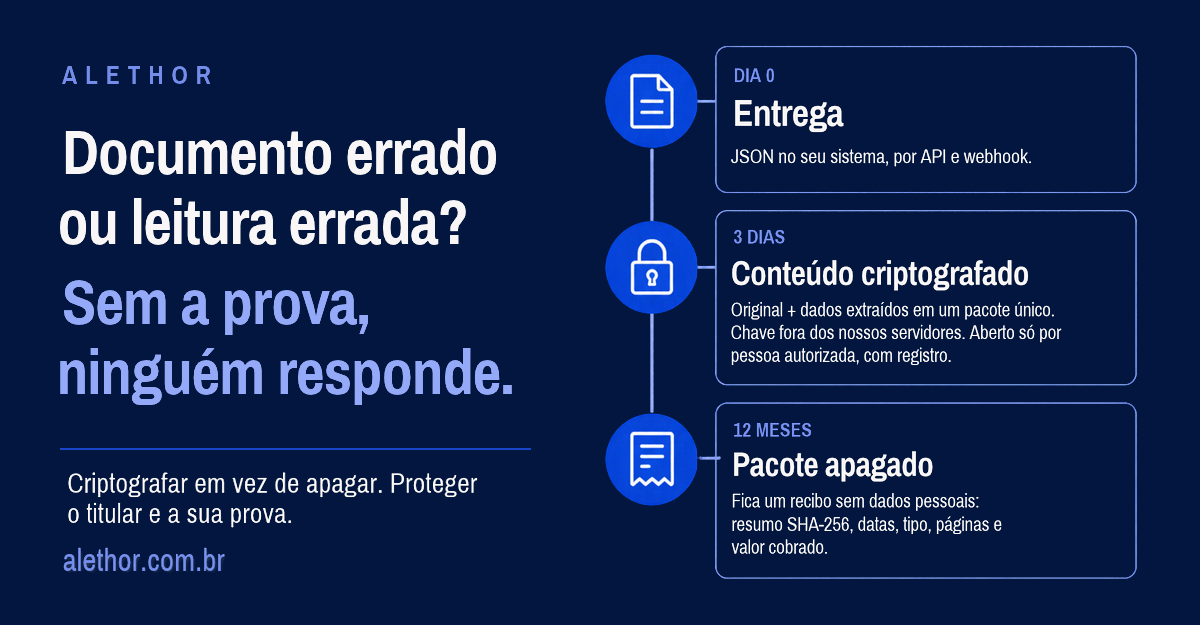
That is why Alethor does not delete the document immediately after delivery. It encrypts it.
3 days after delivery, the original and the extracted data become a single, encrypted package, with the key outside our servers. From then on, no one can access this content via API or screen.
The package is only opened by an authorized person, and only in the event of an extraction dispute, a data subject request forwarded by you, or a legal obligation. Each access is logged.
12 months later, the package is deleted. All that remains is a receipt without personal data, containing the SHA-256 hash of the original and the data, dates, document type, pages, and amount charged.
For the BPO, this protects two things: the data subject, because the data is not exposed; and you, because you still have a way to prove what was read if someone questions it.
Deleting everything immediately seems like the safest way to comply with the LGPD. For anyone who might be questioned later, it is the fastest way to lose evidence.
When an employee disputes an amount today, how long does it take your team to find the document that originated it?
https://alethor.com.br/seguranca
Send us an email!